What is Sibylity?

The Operating System For Population-Scale Cyber Risk

Public health protects millions without a clinician for every person — through screening, self-care, and specialists reserved for the serious cases. Sibylity brings that model to cybersecurity: every team maintains its own security plan with AI guidance, your experts focus where they're truly needed, and Sibylity watches the whole population for the risks that need your expert attention.

Contact Us

Built on Five Principles of Participation

01

Agile & Lean Design

Iterative, low-friction workflows built around how teams actually work.

02

Automating the Tedious

The work people dread gets done automatically.

03

Knowledge at Point of Decision

Insight delivered when it can be acted on — not buried in reports.

04

Psychological Safety

Gaps are improvement opportunities. Honest reporting is safe and rewarded.

05

Gamification

Progress is visible. Contribution is recognized. Participation becomes self-sustaining.

Resource teams build quality security plans in under an hour

What used to take weeks of back-and-forth now happens in a single guided session. Sibylity's QuickPlans walk resource teams through tailored assessments that feel familiar — while building a comprehensive control inventory behind the scenes.

⚡ QuickPlans

Configure guided workflows that match your organization's needs. NIST 800-18 style security plans that any team can complete without security expertise.

🤖 Thia — AI-Powered Guidance

Every user gets integrated support at every decision point. Thia helps teams characterize resources, identify risks, and select appropriate mitigations — knowledge delivered exactly when and where it's needed.

📋 Control Inventory

Document what controls are actually implemented, not just what policies say should exist. User-friendly workflows build systematic documentation automatically.

QuickPlan Session
Step 1: Resource Characterization
Thia guides team through data types, users, and control identification
✓ Complete
Step 2: Risk Identification
Thia recommends relevant risks from your library
✓ Complete
Step 3: Mitigation Selection
Choose from Thia-suggested mitigations or define your own
In Progress
Step 4: Plan Approval & Documentation

Configure once. Scale everywhere.

Your organization is unique. Sibylity adapts to your framework, your language, your way — without requiring custom development.

🏗️ Security Model

Define custom data types, impacts, questions, and assessments. Enable built-in baselines or create your own. Your framework, your language, your way.

🔗 Common Controls

Document shared services and infrastructure controls once, then let resource teams inherit them. When your identity management provides MFA for everyone, document it once.

📌 Control Extension

Go beyond documenting what controls exist — prescribe how to implement them. Give resource teams specific, actionable guidance tailored to your environment.

Your Security Model
Organization-Wide Standards
Baselines · Frameworks · Policies
Resource Team A
Inherits common controls + custom
Resource Team B
Inherits common controls + custom
Resource Team C
Inherits common controls + custom
+ All Others

Your team's AI colleague inside Sibylity

Resource teams don't experience Sibylity as a compliance tool — they experience Thia. She's the one who walks them through QuickPlans, surfaces the right risks for their specific environment, and delivers guidance exactly when it's needed.

But Thia doesn't improvise. Everything she says, every risk she flags, every mitigation she recommends — it all flows directly from the security model your administrators have configured. You define the standards. Thia makes sure every team works in alignment with them.

Teams also meet Del — Thia's ever-present companion and the help icon throughout the app. Whenever someone needs context, a definition, or a nudge in the right direction, Del is there. Together, they make security feel less like a burden and more like something your team actually wants to engage with.
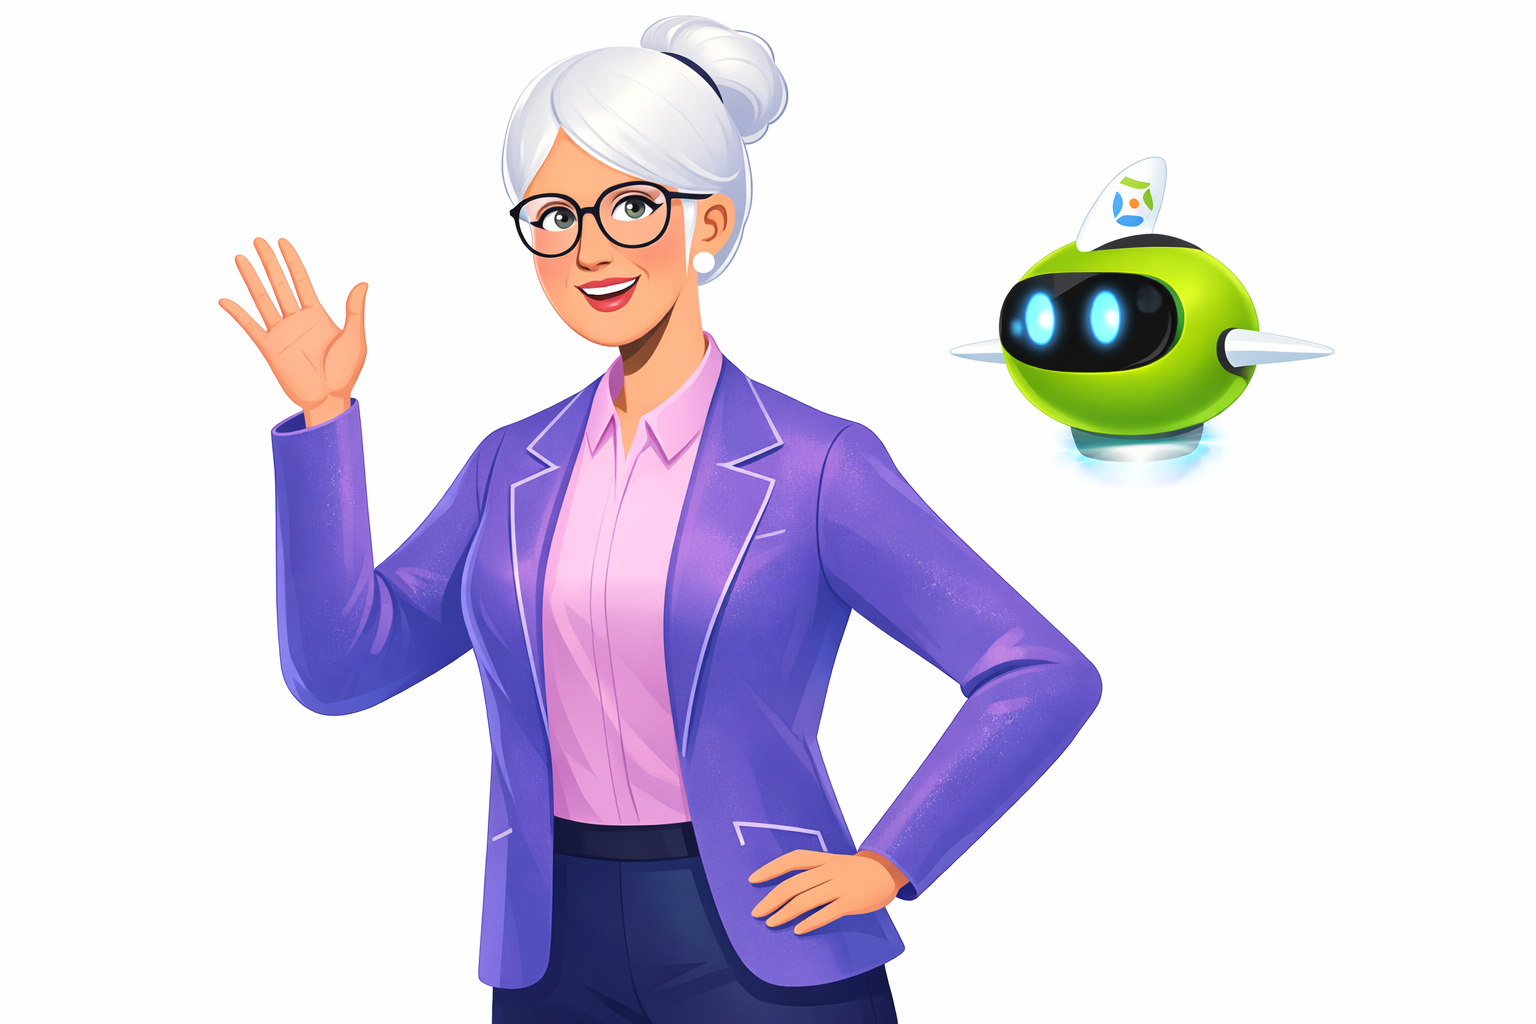
AI-Powered Guidance Configuration-Driven Always Present
Thia, your AI colleague in Sibylity

Everything you need to run a decentralized risk program

From risk identification through remediation, with visibility at every stage.

🎯

Risk Intelligence

Thia analyzes each resource's characteristics and recommends relevant risks. Teams build comprehensive risk registers without security expertise — with every decision documented and defensible.

Identification · Handling · Remediation
🔄

Distributed Execution

Resource teams own resource-specific security plans while security owns the standards. Guided workflows and embedded intelligence enable any team to build a quality plan without deep security knowledge.

Empowerment · Coordination · Oversight
🏆

Engagement & Adoption

Gamification rewards teams for building security plans and closing gaps. Track participation across the organization. Built on Agile and Lean principles, teams actually use the system instead of working around it.

Gamification · Progress Tracking · Behavioral Design
📊

Operational Intelligence

Monitor the complete lifecycle — which projects exist, which have approved security plans, what risks are identified, how they're being handled. Real operational data, not just compliance percentages.

Dashboards · Traceability · GRC Integration
🔬

Syndromic Surveillance

Borrowed from public health: instead of waiting for incidents, Sibylity watches for patterns across the whole population — clusters of the same gap, stalling participation, controls drifting out of date — and surfaces them as early warnings while they're still cheap to fix.

Signals · Patterns · Early Warning
🕸️

Dependency & Ownership Mapping

Every gap traces to a name. Sibylity maps risk across resources, shared common controls, and third parties — so you see not just where a gap is, but who owns it and everyone downstream who inherits it. Fix one common control and the whole population's posture moves.

Resources · Common Controls · Third Parties
What You Can See

Read the population the way an epidemiologist reads a city

Every plan, control, and signal rolls up into a picture of the whole population — not just counts, but where posture is real versus paper, where work stalls, and who needs a closer look. A few of the views leaders reach for:

The Findings-to-Remediation Cascade
Identified 340 · 100%
Owner assigned 316 · 93%
Remediation planned 291 · 86%
In progress 258 · 76%
▼ biggest drop · 25 pts age out here before closing
Closed 173 · 51%

How to read it: findings should flow left to right to closure. They pile up In progress — work gets started but drags, and items age open before they close. That points you straight to the aging findings to chase and the owners to unblock: a throughput problem, not a coverage one.

Security Theater Detector
Reported implemented Backed by evidence
Multi-factor authentication 4-pt gap
Encryption at rest 9-pt gap
Access reviews 34-pt gap
Backup restoration tests 39-pt gap

How to read it: when reported towers over evidenced, the control lives on paper, not in practice. Access reviews and backup tests are where the real exposure is hiding.

Adaptive Oversight
On-time history (older → recent) · met / missed
College of Science
Self-serve
Central IT Services
Self-serve
Facilities Management
Watching
Regional Clinic 7
Flagged

How to read it: clean records run themselves. When a team starts slipping deadlines, Sibylity raises the monitoring — and eases off once they're regular again. Attention follows risk, automatically.

Illustrative views — live dashboards reflect your real population and data.

You maintain oversight without becoming a bottleneck

Sibylity provides the guardrails that make distributed ownership work: intelligent guidance at every step, behavioral monitoring that flags when consultation is needed, and complete audit trails of every decision. Resource teams move independently — and you always know what's happening.

What teams are saying

It's keeping us organized and keeping us focused into finding the right solutions when we have a problem.
LM
Lizeth Mora
Senior Director
That's what I think we get now — beneficial feedback that says we're on the right path, or these are some of the things you can do to get on that path.
DT
Dirk Timmerman
Director of IT
The university finally has a tool that will measurably reduce information security risk to the institution. It is actually fun to use!
TB
Teresa Banks
Information Security Manager

See Sibylity in action

If you believe that people, given the right support, can be your strongest security asset rather than your weakest link, we should talk.